


Get HP HPE7-A02 Dumps Questions Study Exam Guide Mar 10, 2026
HPE7-A02 Premium Exam Engine - Download Free PDF Questions
NEW QUESTION # 52
A company has HPE Aruba Networking gateways that implement gateway IDS/IPS. Admins sometimes check the Security Dashboard, but they want a faster way to discover if a gateway starts detecting threats in traffic.
What should they do?
- A. Set up Webhooks that are attached to the HPE Aruba Networking Central Threat Dashboard.
- B. Use Syslog to integrate the gateways with HPE Aruba Networking ClearPass Policy Manager (CPPM) event processing.
- C. Integrate HPE Aruba Networking ClearPass Device Insight (CPDI) with Central and schedule hourly reports.
- D. Set up email notifications using HPE Aruba Networking Central's global alert settings.
Answer: D
Explanation:
For a faster way to discover if a gateway starts detecting threats in traffic, admins should set up email notifications using HPE Aruba Networking Central's global alert settings. This setup ensures that the security team is promptly informed via email whenever the IDS/IPS on the gateways detects any threats, allowing for immediate investigation and response.
1.Email Notifications: By configuring email notifications, admins can receive real-time alerts directly to their inbox, reducing the time to discover and react to security incidents.
2.Global Alert Settings: HPE Aruba Networking Central's global alert settings allow for customization of alerts based on specific security events and thresholds, providing flexibility in monitoring and response.
3.Proactive Monitoring: This proactive approach ensures that the security team is always aware of potential threats without the need to constantly check the Security Dashboard manually.
NEW QUESTION # 53
You need to set up an HPE Aruba Networking VIA solution for a customer who needs to support 2100 remote employees. The customer wants employees to download their VIA connection profile from the VPNC. Only employees who authenticate with their domain credentials to HPE Aruba Networking ClearPass Policy Manager (CPPM) should be able to download the profile. (A RADIUS server group for CPPM is already set up on the VPNC.) How do you configure the VPNC to enforce that requirement?
- A. Create a new VPN Authentication Profile and then reference CPPM's default server group in that profile.
- B. Reference CPPM's server group in an AAA profile; then, apply that profile to the VPNC's Internet-facing ports.
- C. Set up a VIA Authentication Profile that uses CPPM's server group; reference that profile in the VIA Connection Profile.
- D. Set up a VIA Authentication Profile that uses CPPM's server group; reference that profile in the VIA Web Authentication Profile.
Answer: D
Explanation:
To configure the HPE Aruba Networking VIA solution for remote employees who need to download their VIA connection profile from the VPN Concentrator (VPNC) and ensure that only those who authenticate with their domain credentials through ClearPass Policy Manager (CPPM) can do so, you need to set up a VIA Authentication Profile. This profile should use the CPPM's RADIUS server group. Once the VIA Authentication Profile is created, you need to reference this profile in the VIA Web Authentication Profile.
This configuration ensures that the authentication process requires employees to validate their credentials via CPPM before they can download the VIA connection profile.
NEW QUESTION # 54
You are helping an organization deploy HPE Aruba Networking SSE. What is one reason to recommend that the company install agents on remote users' devices?
- A. To permit admins to manage the HPE Aruba Networking SSE policy rules.
- B. To run threat inspection on clients in a local sandbox rather than in the cloud.
- C. To run posture checks and apply different permissions based on those checks.
- D. To permit users to access private servers using SSH.
Answer: C
Explanation:
* Installing Agents for SSE (Secure Service Edge):
* Agents installed on remote users' devices allow posture checks (e.g., antivirus status, OS version) to ensure compliance.
* Based on the results of the posture checks, different permissions and security policies can be applied dynamically.
* This improves the security posture of remote users before granting access to resources.
* Option A: Correct. Agents enable posture checks and enforce conditional access based on compliance.
* Option B: Incorrect. Admins manage SSE policies centrally, not via agents.
* Option C: Incorrect. Access to private servers via SSH does not require agents; it relies on policies and tunnels.
* Option D: Incorrect. Local sandboxing is generally a function of endpoint protection solutions, not SSE agents.
NEW QUESTION # 55
You have created this rule in an HPE Aruba Networking ClearPass Policy Manager (CPPM) service's enforcement policy: IF Authorization [Endpoints Repository] Conflict EQUALS true THEN apply "quarantine_profile" What information can help you determine whether you need to configure cluster-wide profiler parameters to ignore some conflicts?
- A. Whether the company has rare Internet of Things (loT) devices
- B. Whether some devices are incapable of captive portal or 802.1X authentication
- C. Whether some devices are running legacy operating systems
- D. Whether the company has devices that use PXE boot
Answer: D
Explanation:
When you have created a rule in a ClearPass Policy Manager (CPPM) service's enforcement policy to quarantine devices with endpoint conflicts, it is important to consider whether the company has devices that use PXE boot. PXE booting devices can create conflicts in the profiler because they may temporarily have different network attributes (e.g., MAC address or IP address) before fully booting and obtaining their final configuration. Understanding whether PXE boot is in use can help determine if profiler parameters need to be adjusted to ignore such temporary conflicts, ensuring that devices are not incorrectly quarantined.
NEW QUESTION # 56
You have enabled "rogue AP containment" in the Wireless IPS settings for a company's HPE Aruba Networking APs. What form of containment does HPE Aruba Networking recommend?
- A. Wired containment
- B. Wireless tarpit and wired containment
- C. Wireless tarpit only
- D. Wireless deauthentication only
Answer: D
Explanation:
* Rogue AP Containment Methods:
* HPE Aruba Networking recommends using wireless deauthentication as the preferred method for rogue AP containment.
* Deauthentication sends deauth frames to clients connected to rogue APs, causing them to disconnect. This method is effective without introducing unnecessary disruptions to the wired infrastructure.
* Key Points:
* Wireless Deauthentication is simple, efficient, and widely supported across client devices.
* Tarpit Containment is more aggressive and may cause unintentional disruptions to legitimate clients.
* Wired Containment involves blocking traffic at the switch level but is complex and may impact legitimate infrastructure traffic.
* Option Analysis:
* Option A: Correct. Wireless deauthentication is the recommended method as it targets rogue AP clients without excessive network impact.
* Option B: Incorrect. Combining wireless tarpit and wired containment is overkill and not typically recommended.
* Option C: Incorrect. Wireless tarpit can be effective but is generally not the first choice due to its aggressive nature.
* Option D: Incorrect. Wired containment is more complex and reserved for specific use cases, not general recommendations.
NEW QUESTION # 57
You are setting up an HPE Aruba Networking VIA solution for a company. You need to configure access control policies for applications and resources that remote clients can access when connected to the VPN.
Where on the VPNC should you configure these policies?
- A. In the cloud security settings using IPsec maps
- B. In the roles to which VIA clients are assigned after IKE authentication
- C. In the roles to which VIA clients are assigned after VIA Web authentication
- D. In the tunneled network settings within the VIA Connection Profile
Answer: B
Explanation:
To configure access control policies for applications and resources that remote clients can access when connected to the VPN, you should configure these policies in the roles to which VIA clients are assigned after IKE (Internet Key Exchange) authentication on the VPNC. These roles define the permissions and access controls for the clients once they are authenticated, ensuring that they can only access the applications and resources allowed by their assigned roles.
1.IKE Authentication: After IKE authentication, clients are assigned specific roles that determine their access privileges.
2.Role-Based Access Control: By configuring access control policies within these roles, you can granularly control what resources and applications the remote clients can access over the VPN.
3.Security: This method ensures that access is managed securely and dynamically based on the role assigned to each client after successful authentication.
Reference: Aruba's VPN and VIA deployment guides provide detailed instructions on configuring roles and access control policies for remote VPN clients.
NEW QUESTION # 58
A company lacks visibility into the many different types of user and loT devices deployed in its internal network, making it hard for the security team to address those devices.
Which HPE Aruba Networking solution should you recommend to resolve this issue?
- A. HPE Aruba Networking Network Analytics Engine (NAE)
- B. HPE Aruba Networking Mobility Conductor
- C. HPE Aruba Networking ClearPass OnBoard
- D. HPE Aruba Networking ClearPass Device Insight (CPDI)
Answer: D
Explanation:
For a company that lacks visibility into various types of user and IoT devices on its internal network, HPE Aruba Networking ClearPass Device Insight (CPDI) is the recommended solution. CPDI provides comprehensive visibility and profiling of all devices connected to the network. It uses machine learning and AI to identify and classify devices, offering detailed insights into their behavior and characteristics. This enhanced visibility enables the security team to effectively monitor and manage network devices, improving overall network security and compliance.
Reference: Aruba's documentation on ClearPass Device Insight outlines its capabilities in device discovery, profiling, and security posture assessment, making it ideal for environments with diverse and numerous network-connected devices.
NEW QUESTION # 59
Which issue can an HPE Aruba Networking Secure Web Gateway (SWG) solution help customers address?
- A. The organization currently has no way to prevent users from exfiltrating sensitive data from SaaS applications.
- B. The organization needs a faster way to quarantine clients that have generated threats, as detected by third-party firewalls.
- C. Remote workers need access to private data center applications without exposing those applications to unauthorized users.
- D. Hybrid workers are exposing their computers to risky internet sites and infection by malware when they work from home.
Answer: D
Explanation:
An HPE Aruba Networking Secure Web Gateway (SWG) is designed to provide secure internet access by monitoring and controlling web traffic. It primarily focuses on protecting users from malicious content and ensuring compliance with corporate security policies, particularly for hybrid and remote workers.
Explanation of Each Option
A: The organization needs a faster way to quarantine clients that have generated threats, as detected by third-party firewalls.
* Incorrect:
* Quarantining clients based on detected threats is typically managed by endpoint detection and response (EDR) solutions or next-generation firewalls (NGFWs).
* While an SWG can monitor and block risky web activity, it does not manage threat quarantine actions directly.
B: Hybrid workers are exposing their computers to risky internet sites and infection by malware when they work from home.
* Correct:
* SWGs monitor and control web traffic to block malicious websites and prevent exposure to malware.
* They enforce web usage policies even when users work remotely, protecting against phishing, drive-by downloads, and other web-based threats.
* With the proliferation of hybrid work environments, an SWG ensures that users are protected from risky sites regardless of their location.
C: Remote workers need access to private data center applications without exposing those applications to unauthorized users.
* Incorrect:
* This use case falls under secure access service edge (SASE) solutions with Zero Trust Network Access (ZTNA), not an SWG.
* ZTNA focuses on granting secure, conditional access to applications, while SWGs focus on internet traffic security.
D: The organization currently has no way to prevent users from exfiltrating sensitive data from SaaS applications.
* Incorrect:
* Data loss prevention (DLP) tools or cloud access security brokers (CASBs) are designed for monitoring and preventing data exfiltration from SaaS applications.
* While SWGs can block access to specific websites or categories, they do not offer advanced DLP capabilities for SaaS environments.
References
* Aruba Secure Web Gateway Documentation.
* HPE Aruba SASE Solutions Guide.
* Best Practices for Hybrid Workforce Security with Aruba SWG.
NEW QUESTION # 60
A company wants HPE Aruba Networking ClearPass Policy Manager (CPPM) to respond to Syslog messages from its Check Point firewall. You have added the firewall as an event source and set up an event service. However, test Syslog messages are not triggering the expected actions.
What is one CPPM setting that you should check?
- A. Ingress Event Dictionaries for Check Point messages are enabled.
- B. The Check Point Extension is installed through ClearPass Guest.
- C. ClearPass Device Insight integration is disabled.
- D. The CoA delay value is set to 0 on the server.
Answer: A
Explanation:
To ensure that HPE Aruba Networking ClearPass Policy Manager (CPPM) responds correctly to Syslog messages from a Check Point firewall, you need to check that the Ingress Event Dictionaries for Check Point messages are enabled. These dictionaries are necessary for CPPM to properly interpret and respond to the Syslog messages received from the firewall.
1.Event Dictionaries: Ingress Event Dictionaries allow CPPM to understand the specific format and content of Syslog messages from various sources, such as Check Point firewalls.
2.Message Interpretation: Without these dictionaries enabled, CPPM may not correctly interpret the Syslog messages, leading to a failure in triggering the expected actions.
3.Configuration Check: Ensuring that the dictionaries are enabled is crucial for the proper functioning of the event service and accurate response to security events.
NEW QUESTION # 61
A company is implementing HPE Aruba Networking Wireless IDS/IPS (WIDS/WIPS) on its AOS-10 APs, which are managed in HPE Aruba Networking Central.
What is one requirement for enabling detection of rogue APs?
- A. A manual radio profile that enables non-regulatory channels
- B. Each VLAN in the network assigned on at least one AP's or AM's port
- C. One AM deployed for every one AP deployed
- D. A Foundation with Security license for each of the APs
Answer: D
Explanation:
To enable the detection of rogue APs with HPE Aruba Networking Wireless IDS/IPS (WIDS/WIPS) on AOS-
10 APs managed in HPE Aruba Networking Central, each AP must have a Foundation with Security license.
This license enables advanced security features, including rogue AP detection, which is crucial for maintaining a secure wireless environment and protecting against unauthorized access points.
NEW QUESTION # 62
A company has HPE Aruba Networking APs and AOS-CX switches. The APs bridge wireless traffic. They receive DHCP IP addresses on VLAN 18. Wireless users are assigned to VLAN 12.
The company wants the APs to start using 802.1X authentication on their switch ports. You are configuring the port-access role to which the APs are assigned after authentication.
What is one recommended setting for that role?
- A. No trust for DSCP
- B. Auth-mode left at client-mode
- C. Trust for DSCP
- D. Access VLAN 18 with no support for VLAN 12
Answer: C
Explanation:
When a switch port connects to a wireless AP that bridges multiple client VLANs, best practice is to:
* Keep the VLAN/trunking configuration on the interface (not forced by the role), so that both VLAN 18 (AP management) and VLAN 12 (clients) are supported.
* Enable trust of DSCP on the AP uplink so that QoS markings from the AP (voice, real-time traffic) are honored end-to-end, instead of being remarked or reset at the switch. Aruba wired-access and campus deployment guides repeatedly recommend trusting DSCP on AP uplinks so that WMM/802.11e markings are preserved.
Option D ("Access VLAN 18 with no support for VLAN 12") would break the design because the AP needs to carry client VLAN 12 across its uplink. Option C (auth-mode client-mode) is about how many supplicants per port are authenticated; it is not the key "recommended" setting in this scenario, and Aruba designs typically focus QoS for AP uplinks via trust settings.
Therefore, the recommended role setting here is to trust DSCP on the AP's authenticated role # Option B.
NEW QUESTION # 63
A company has AOS-CX switches. The company wants to make it simpler and faster for admins to detect denial of service (DoS) attacks, such as ping or ARP floods, launched against the switches.
What can you do to support this use case?
- A. Enabling debugging of security functions on the switches.
- B. Configure the switches to implement RADIUS accounting to HPE Aruba Networking ClearPass and enable HPE Aruba Networking ClearPass Insight.
- C. Deploy an NAE agent on the switches to monitor control plane policing (CoPP).
- D. Implement ARP inspection on all VLANs that support end-user devices.
Answer: C
Explanation:
Why Monitoring Control Plane Policing (CoPP) with an NAE Agent Is Effective for Detecting DoS Attacks
* Control Plane Policing (CoPP): AOS-CX switches use CoPP to protect the CPU from excessive traffic caused by DoS attacks (e.g., ARP floods, ICMP floods). CoPP enforces rate limits and drops malicious traffic at the control plane level.
* NAE (Network Analytics Engine) Agent:
* The NAE on AOS-CX switches can monitor CoPP counters in real time and trigger alerts if thresholds for certain traffic types (e.g., ICMP, ARP) are exceeded.
* Admins can use NAE to automate detection and respond faster to DoS attacks.
Analysis of Each Option
A: Deploy an NAE agent on the switches to monitor control plane policing (CoPP):
* Correct:
* NAE agents provide real-time visibility into CoPP behavior, helping detect DoS attacks more quickly.
* By analyzing CoPP statistics, the NAE can pinpoint abnormal traffic patterns and alert admins.
* This is the most efficient and scalable solution for this use case.
B: Configure the switches to implement RADIUS accounting to HPE Aruba Networking ClearPass and enable HPE Aruba Networking ClearPass Insight:
* Incorrect:
* While ClearPass can provide visibility into user authentication and device activity, it is not specifically designed to detect or mitigate DoS attacks against switches.
C: Implement ARP inspection on all VLANs that support end-user devices:
* Incorrect:
* ARP inspection helps mitigate ARP spoofing or poisoning, but it does not directly address detection of DoS attacks like ICMP or ARP floods.
* It is a preventative measure, not a detection tool.
D: Enabling debugging of security functions on the switches:
* Incorrect:
* Debugging logs can help troubleshoot specific issues but are not practical for real-time detection of DoS attacks.
* Enabling debugging can overload the switch and is not suitable for proactive monitoring.
Final Recommendation
Deploying an NAE agent to monitor CoPP is the best solution because it provides real-time detection, alerting, and insights into traffic patterns that indicate DoS attacks.
References
* AOS-CX Network Analytics Engine (NAE) Configuration Guide.
* HPE Aruba AOS-CX Control Plane Policing Documentation.
* Best Practices for Protecting Switches Against DoS Attacks in Aruba Networks.
NEW QUESTION # 64
An admin has configured an AOS-CX switch with these settings:
port-access role employees
vlan access name employees
This switch is also configured with CPPM as its RADIUS server.
Which enforcement profile should you configure on CPPM to work with this configuration?
- A. HPE Aruba Networking Downloadable Role Enforcement type with role name set to "employees"
- B. RADIUS Enforcement type with Aruba-User-Role VSA set to "employees"
- C. HPE Aruba Networking Downloadable Role Enforcement type with gateway role name set to
"employees" - D. RADIUS Enforcement type with HPE-User-Role VSA set to "employees"
Answer: B
Explanation:
To ensure that the AOS-CX switch properly assigns the "employees" role when using CPPM (ClearPass Policy Manager) as the RADIUS server, you should configure a RADIUS Enforcement profile on CPPM with the Aruba-User-Role VSA (Vendor-Specific Attribute) set to "employees". This configuration ensures that when an endpoint authenticates, CPPM sends the appropriate role assignment to the AOS-CX switch, which then applies the corresponding policies and VLAN settings defined for the "employees" role.
Reference: Aruba's ClearPass documentation and AOS-CX configuration guides detail the integration and configuration of RADIUS enforcement profiles using Aruba-User-Role VSAs for role-based access control.
NEW QUESTION # 65
A company is using HPE Aruba Networking ClearPass Device Insight (CPDI) (the standalone application).
You have identified a device, which is currently
classified as one type, but you want to classify it as a custom type. You also want to classify all devices with similar attributes as this type, both already-discovered devices and new devices discovered later.
What should you do?
- A. In the device details, select filter, create a user tag based on the device attributes, and save the tag.
- B. Create a user rule from the Generic Devices page, select the desired attributes for the rule, and choose
"Save." - C. Create a user tag from the Generic Devices page, select the desired attributes for the tag, and save the tag.
- D. In the device details, select reclassify, create a user rule based on its attributes, and choose "Save & Reclassify."
Answer: D
Explanation:
When using HPE Aruba Networking ClearPass Device Insight (CPDI) and you need to reclassify a device to a custom type and apply this classification to all devices with similar attributes, both already discovered and newly discovered, you should follow these steps:
1.Navigate to the device details in CPDI.
2.Select the option to reclassify the device.
3.Create a user rule based on the desired attributes of the device.
4.Choose the "Save & Reclassify" option.
This process ensures that the device is reclassified according to the new custom type and that the rule is applied to all existing and future devices with matching attributes, maintaining consistent classification across the network.
NEW QUESTION # 66
An admin has configured an AOS-CX switch with these settings:
port-access role employees
vlan access name employees
This switch is also configured with CPPM as its RADIUS server.
Which enforcement profile should you configure on CPPM to work with this configuration?
- A. HPE Aruba Networking Downloadable Role Enforcement type with role name set to "employees"
- B. RADIUS Enforcement type with Aruba-User-Role VSA set to "employees"
- C. HPE Aruba Networking Downloadable Role Enforcement type with gateway role name set to
"employees" - D. RADIUS Enforcement type with HPE-User-Role VSA set to "employees"
Answer: B
Explanation:
To ensure that the AOS-CX switch properly assigns the "employees" role when using CPPM (ClearPass Policy Manager) as the RADIUS server, you should configure a RADIUS Enforcement profile on CPPM with the Aruba-User-Role VSA (Vendor-Specific Attribute) set to "employees". This configuration ensures that when an endpoint authenticates, CPPM sends the appropriate role assignment to the AOS-CX switch, which then applies the corresponding policies and VLAN settings defined for the "employees" role.
NEW QUESTION # 67
A company wants HPE Aruba Networking ClearPass Policy Manager (CPPM) to periodically poll Microsoft Endpoint Manager (formerly Intune) for attributes about its managed clients.
What should you do on ClearPass to permit this integration?
- A. Install the Intune extension from ClearPass Guest
- B. Configure Endpoint Manager (Intune) as an event source on CPPM
- C. Import the Intune dictionary into the ClearPass dictionaries
- D. Create an Intune authentication source on CPPM
Answer: D
Explanation:
For ClearPass to periodically query Microsoft Intune / Endpoint Manager for device attributes (compliance, owner, OS, etc.), you must configure Intune as an authentication source in Policy Manager. The ClearPass- Intune integration is implemented through an API-based auth source which CPPM polls on a schedule; it is not done via Guest extensions or syslog/event sources.
Aruba's Intune integration guides describe configuring a "Microsoft Intune" (or "Endpoint Manager") authentication source in ClearPass and supplying the Azure app registration details so CPPM can poll Intune via Microsoft Graph.
* Option A is incorrect: the Intune integration is not a ClearPass Guest extension.
* Option B is insufficient: adding dictionaries only defines attributes; it does not enable scheduled polling.
* Option D is incorrect: Intune is not used as a syslog/event source for this use case; ClearPass initiates the polling via the authentication source.
Therefore, the correct configuration step is: Create an Intune authentication source on CPPM (Option C).
NEW QUESTION # 68
A company lacks visibility into the many different types of user and loT devices deployed in its internal network, making it hard for the security team to address those devices.
Which HPE Aruba Networking solution should you recommend to resolve this issue?
- A. HPE Aruba Networking Network Analytics Engine (NAE)
- B. HPE Aruba Networking Mobility Conductor
- C. HPE Aruba Networking ClearPass OnBoard
- D. HPE Aruba Networking ClearPass Device Insight (CPDI)
Answer: D
Explanation:
For a company that lacks visibility into various types of user and IoT devices on its internal network, HPE Aruba Networking ClearPass Device Insight (CPDI) is the recommended solution. CPDI provides comprehensive visibility and profiling of all devices connected to the network. It uses machine learning and AI to identify and classify devices, offering detailed insights into their behavior and characteristics. This enhanced visibility enables the security team to effectively monitor and manage network devices, improving overall network security and compliance.
NEW QUESTION # 69
HPE Aruba Networking ClearPass Policy Manager (CPPM) uses a service to authenticate clients. You are now adding the Endpoints Repository as an authorization source for the service, and you want to add rules to the service's policies that apply different access levels based, in part, on a client's device category. You need to ensure that CPPM can apply the new correct access level after discovering new clients' categories.
What should you enable on the service?
- A. The Profile Endpoints option in the Service tab
- B. The Audit End-host option in the Service tab
- C. The Use cached Roles and Posture attributes from previous sessions option in the Enforcement tab
- D. The Posture Compliance option in the Service tab
Answer: A
Explanation:
To ensure that HPE Aruba Networking ClearPass Policy Manager (CPPM) can apply the correct access levels based on a client's device category after discovering new clients, you need to enable the "Profile Endpoints" option in the Service tab. This option allows CPPM to profile and categorize endpoints dynamically, ensuring that the appropriate access levels are applied based on the device's characteristics.
Enabling this feature ensures that new devices are accurately profiled and that access policies can be enforced based on the updated device information.
NEW QUESTION # 70
A company has HPE Aruba Networking APs (AOS-10), which authenticate clients to HPE Aruba Networking ClearPass Policy Manager (CPPM). CPPM is set up to receive a variety of information about clients' profile and posture. New information can mean that CPPM should change a client's enforcement profile.
What should you set up on the APs to help the solution function correctly?
- A. In the security settings, configure dynamic denylisting.
- B. In the RADIUS server settings for CPPM, enable querying the authentication status.
- C. In the WLAN profiles, enable interim RADIUS accounting.
- D. In the RADIUS server settings for CPPM, enable Dynamic Authorization.
Answer: D
Explanation:
To ensure that HPE Aruba Networking APs (AOS-10) properly interact with HPE Aruba Networking ClearPass Policy Manager (CPPM) and dynamically update a client's enforcement profile based on new profile and posture information, you should enable Dynamic Authorization in the RADIUS server settings for CPPM. This allows ClearPass to send Change of Authorization (CoA) requests to the APs, prompting them to reapply the appropriate enforcement profiles based on updated information.
1.Dynamic Authorization: Enabling this feature allows ClearPass to dynamically push changes to the APs whenever there is new relevant information about a client's profile or posture.
2.Change of Authorization (CoA): This mechanism ensures that clients are assigned the correct enforcement profiles in real-time, based on the latest data.
3.Enhanced Policy Enforcement: This setup helps in maintaining accurate and up-to-date policy enforcement for clients on the network.
Reference: ClearPass and AOS-10 documentation on RADIUS server settings and dynamic authorization explain the process and benefits of enabling Dynamic Authorization for real-time policy updates.
NEW QUESTION # 71
A company uses HPE Aruba Networking ClearPass Policy Manager (CPPM) as a TACACS+ server to authenticate managers on its AOS-CX switches. The company wants CPPM to control which commands managers are allowed to enter.
Which service must you add to the managers' TACACS+ enforcement profile?
- A. ARAP
- B. Cpass:HTTP
- C. Shell
- D. Aruba:Common
Answer: C
Explanation:
To control which commands managers are allowed to execute on AOS-CX switches using ClearPass Policy Manager (CPPM) as a TACACS+ server, you must configure the Shell service in the TACACS+ enforcement profile. The Shell service provides the ability to define granular access controls for commands. It supports policy-driven command authorization, which is essential in controlling administrative tasks based on roles.
References
* Official HPE Aruba ClearPass documentation on TACACS+ integration and command authorization.
* Industry best practices for AAA (Authentication, Authorization, and Accounting) configuration in network security architectures.
NEW QUESTION # 72
Refer to Exhibit: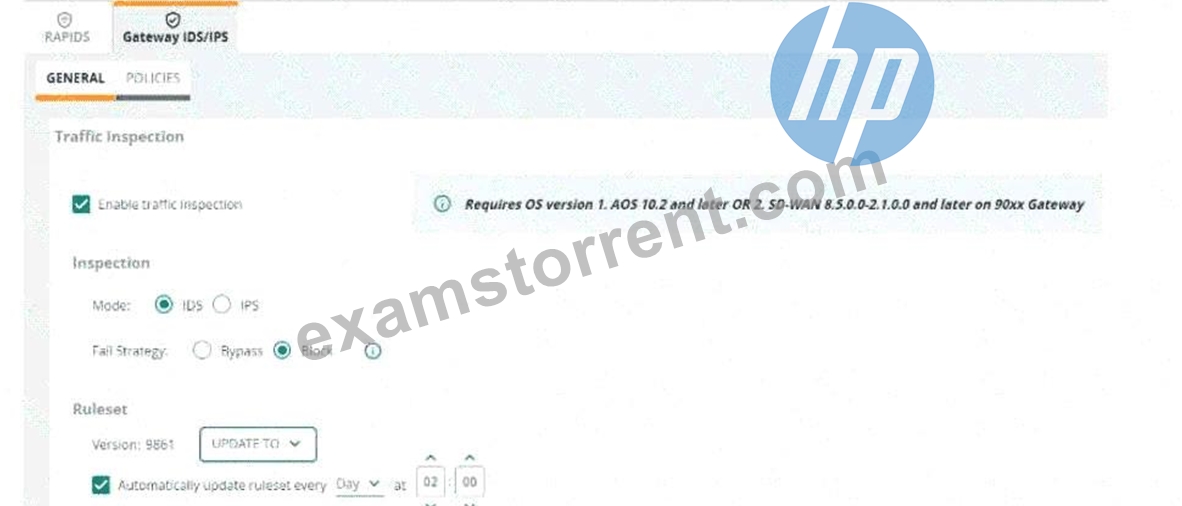
An HPE Aruba Networking 9x00 gateway is part of an HPE Aruba Networking Central group that has the settings shown in the exhibit. What would cause the gateway to drop traffic as part of its IDPS settings?
- A. Its site-to-site VPN connections failing
- B. Traffic matching a rule in the active ruleset
- C. Its IDPS engine failing
- D. Traffic showing anomalous behavior
Answer: B
Explanation:
1. IDPS Mode Configuration Overview
The exhibit shows the HPE Aruba Networking Central settings for the Gateway IDS/IPS configuration:
* Mode: Configured for Intrusion Prevention System (IPS), meaning that the gateway actively blocks traffic identified as threats.
* Fail Strategy: Configured to Block, meaning that if the gateway cannot determine the traffic's nature due to a system issue, it will block the traffic.
* Ruleset: The gateway uses a predefined set of intrusion detection/prevention rules (ruleset version
9861), which is updated automatically every day.
2. Traffic Evaluation in IPS Mode
In IPS mode, the gateway analyzes traffic against the active ruleset:
* If traffic matches a rule in the ruleset and is deemed malicious, the gateway will drop the traffic as part of its prevention mechanism.
* The ruleset defines specific conditions (e.g., signatures of known attacks, protocol anomalies) under which traffic should be blocked.
3. Explanation of Each Option
* A. Its site-to-site VPN connections failing:
* Incorrect:
* Site-to-site VPN connection issues do not directly trigger traffic drops under IDPS settings.
* IDPS is focused on detecting and preventing malicious activity, not general connectivity issues.
* B. Traffic matching a rule in the active ruleset:
* Correct:
* In IPS mode, the gateway drops traffic that matches any predefined rules in the active ruleset.
* For example, if traffic matches the signature of a known exploit or attack, it is immediately blocked.
* C. Its IDPS engine failing:
* Incorrect:
* The fail strategy determines how the gateway behaves in the event of an IDPS engine failure.
* In this case, the fail strategy is set to Block, but this applies only if the engine itself fails, not as a proactive traffic drop mechanism.
* D. Traffic showing anomalous behavior:
* Incorrect:
* While anomalous behavior may be logged or flagged, it does not necessarily lead to traffic drops unless it matches a specific rule in the active ruleset.
* Anomaly detection alone is not sufficient for IPS action without explicit rule matches.
Final Outcome:
Traffic is dropped only when it matches a rule in the active ruleset, ensuring targeted prevention of malicious activity.
References
* Aruba Gateway IDS/IPS Configuration Guide.
* Aruba Central Ruleset Management Documentation.
* Best Practices for Configuring Fail Strategies in IPS Mode.
NEW QUESTION # 73
......
Free HPE7-A02 Exam Braindumps HP Pratice Exam: https://troytec.examstorrent.com/HPE7-A02-exam-dumps-torrent.html