Free Demo


About Palo Alto Networks PCNSE6 Exam Braindumps
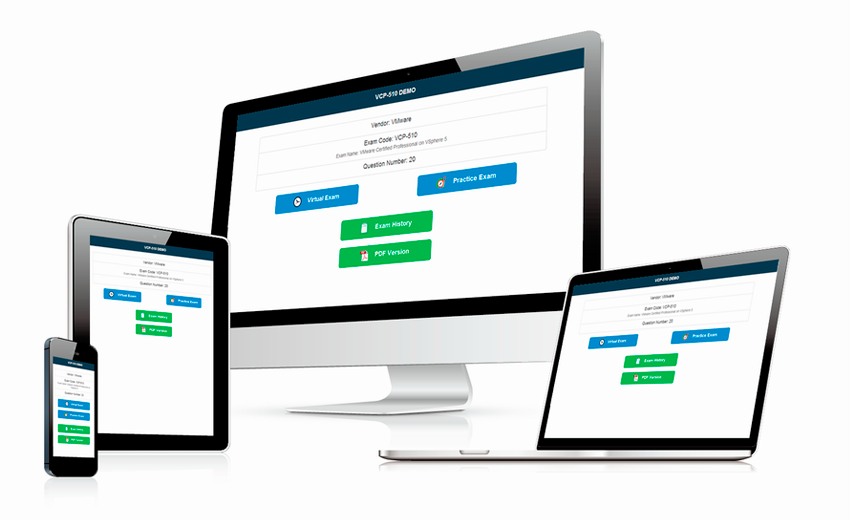
Choosing study material is easier when you can inspect it first. The Palo Alto Networks Certified Network Security Engineer 6 demo on ExamsTorrent is free to download, and it demonstrates both the printable PDF and the interactive engine that hosts the 60 practice questions.
Palo Alto Networks PCNSE6 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Deploy and Configure Core Components | 20% | - Firewall deployment
|
| Manage and Operate | 16% | - Operations and monitoring
|
| Deploy and Configure Features and Subscriptions | 17% | - Advanced security services
|
| Core Concepts | 12% | - Palo Alto Networks platform components
|
| Troubleshooting | 20% | - Troubleshooting methodologies
|
| Deploy and Configure Firewalls Using Panorama | 15% | - Panorama management
|
What Candidates Ask About Palo Alto Networks Certified Network Security Engineer 6
The Palo Alto Networks Certified Network Security Engineer 6 content is the same across all three formats: a printable PDF, a software engine, and an online engine. The free demo lets you try each interface before buying, so you can pick the one that matches how you study rather than guessing.
The package contains 60 practice questions for the PCNSE6 exam, all verified by our IT experts. A free demo is available so you can review the style before you buy.
- Deploy and Configure Core Components (20%)
- Core Concepts (12%)
- Troubleshooting (20%)
Use the weights above to divide your study time where it matters most.
The engine presents Palo Alto Networks Certified Network Security Engineer 6 questions in random order, so each session feels like a fresh test rather than a memorized list. After every simulated exam you receive a score, and your errors are clearly marked, which makes it easy to see your weak and strong areas and build a focused study plan.
The real PCNSE6 exam gives you 90 minutes minutes for Approximately 75 questions. The engine lets you rehearse under the same kind of time pressure, so pacing decisions become automatic.
To pass PCNSE6 you need Not publicly disclosed, and the official fee is USD 175. Setting the target score early makes it easier to measure your progress in practice tests.
No mandatory prerequisite exam is officially required. Hands-on experience with PAN-OS and Palo Alto Networks firewalls is strongly recommended. PCNSA knowledge is beneficial.
Palo Alto Networks Certified Network Security Engineer 6 Sample Questions:
Palo Alto Networks maintains a dynamic database of malicious domains. Which two Security Platform components use this database to prevent threats? Choose 2 answers
- A. Brute-force signatures
- B. DNS-based command-and-control signatures
- C. BrightCloud URL Filtering
- D. PAN-DB URL Filtering
Correct Answer: B,D 🗳️
Explanation: Only visible for ExamsTorrent members. You can sign-up / login (it's free).
Which two statements are true about DoS Protection Profiles and Policies? Choose 2 answers
- A. They mitigate against SYN, UDP, ICMP, ICMPv6, and other IP Flood attacks by utilizing "random early drop".
- B. They mitigate against SYN, UDP, ICMP, ICMPv6, and other IP Flood attacks. They provide resource protection by limiting the number of sessions that can be used.
- C. They mitigate against SYN, UDP, ICMP, ICMPv6, and other IP Flood attacks on a zone basis, regardless of interface(s). They provide reconnaissance protection against TCP/UDP port scans and host sweeps.
- D. They mitigate against volumetric attacks that leverage known vulnerabilities, brute force methods, amplification, spoofing, and other vulnerabilities.
Correct Answer: A,B 🗳️
Explanation: Only visible for ExamsTorrent members. You can sign-up / login (it's free).
A company has a web server behind their Palo Alto Networks firewall that they would like to make accessible to the public. They have decided to configure a destination NAT Policy rule.
Given the following zone information:
-DMZzone: DMZ-L3 -Public zone: Untrust-L3 -Web server zone: Trust-L3 -Public IP address (Untrust-L3): 1.1.1.1 -Private IP address (Trust-L3): 192.168.1.50
What should be configured as the destination zone on the Original Packet tab of the NAT Policy rule?
- A. DMZ-L3
- B. Trust-L3
- C. Any
- D. Untrust-L3
Correct Answer: D 🗳️
Where can the maximum concurrent SSL VPN Tunnels be set for Vsys2 when provisioning a Palo Alto Networks firewall for multiple virtual systems?
- A. In the GUI under Device->Virtual Systems->Vsys2->Resource
- B. In the GUI under Network->Global Protect->Portal->Vsys2
- C. In the GUI under Device->Setup->Session->Session Settings
- D. In the GUI under Network->Global Protect->Gateway->Vsys2
Correct Answer: A 🗳️
Explanation: Only visible for ExamsTorrent members. You can sign-up / login (it's free).
The WildFire Cloud or WF-500 appliance provide information to which two Palo Alto Networks security services? Choose 2 answers
- A. GlobalProtect Data File
- B. Threat Prevention
- C. App-ID
- D. PAN-OS
- E. URL Filtering
Correct Answer: A,B 🗳️
Explanation: Only visible for ExamsTorrent members. You can sign-up / login (it's free).
Viewing page 1 out of 12 pages.
Viewing questions 1-5 out of 60 questions.